Outlook for iOS is dropping support for anything older than iOS 26 - after iOS 27 ships, with rollout starting mid-September 2026 and wrapping up by late September 2026, devices on iOS 18 or earlier stop getting Outlook updates and will eventually lose mail/calendar sync. iPadOS 18 and watchOS 11 hit the same cutoff. No configuration changes are needed on your end, but customers should pull their mobile device inventory now, flag anyone on unsupported versions, and push them to upgrade to iOS 26+ before the window closes to avoid sync interruptions.
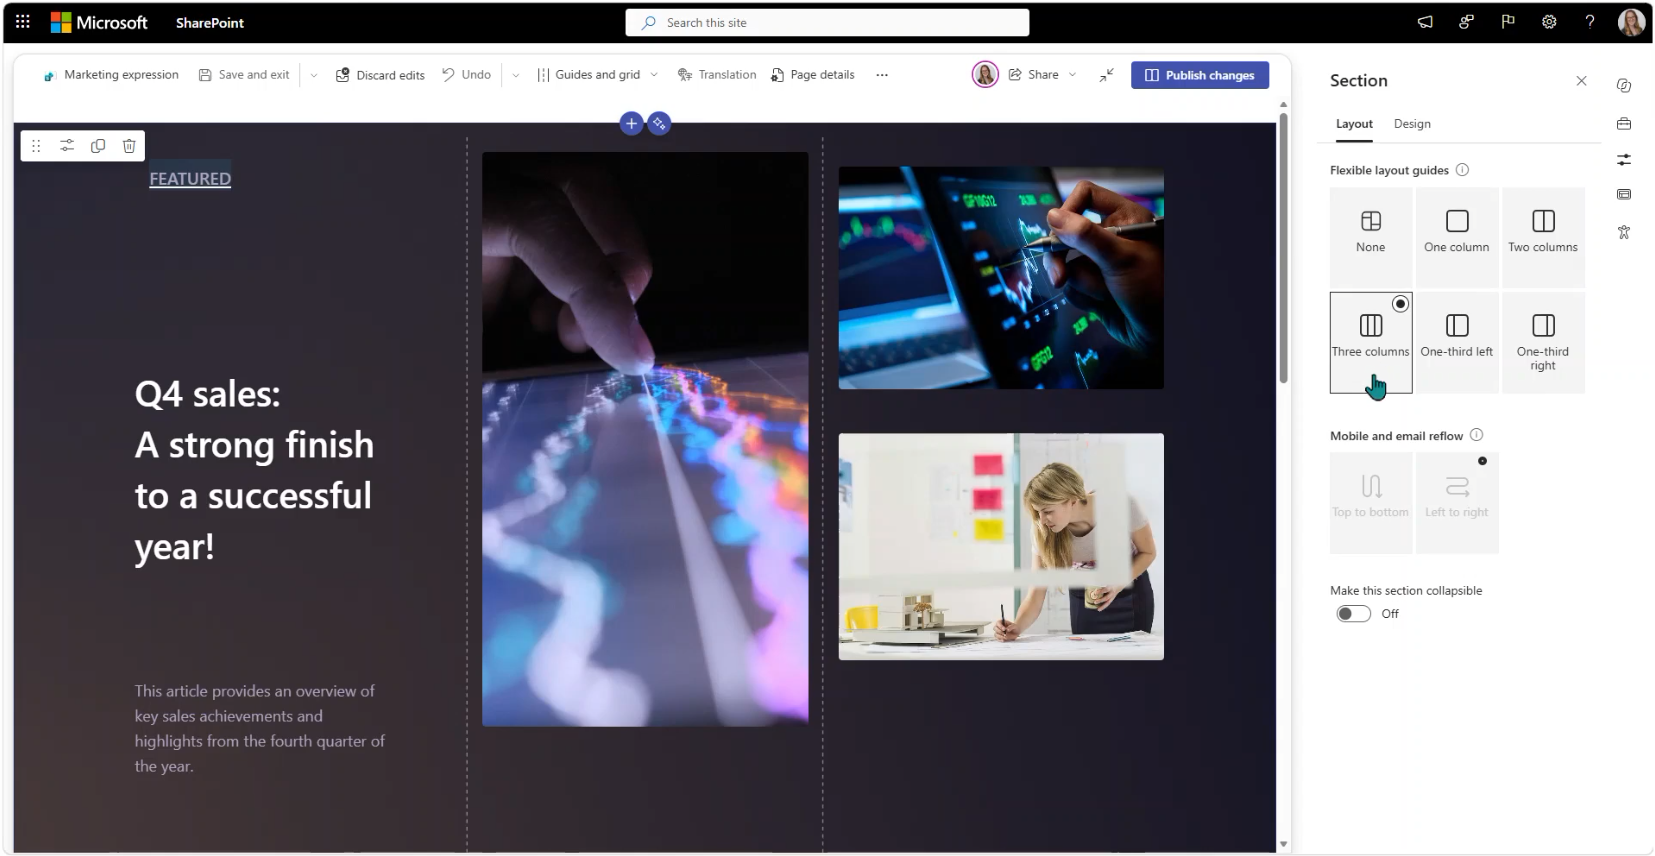
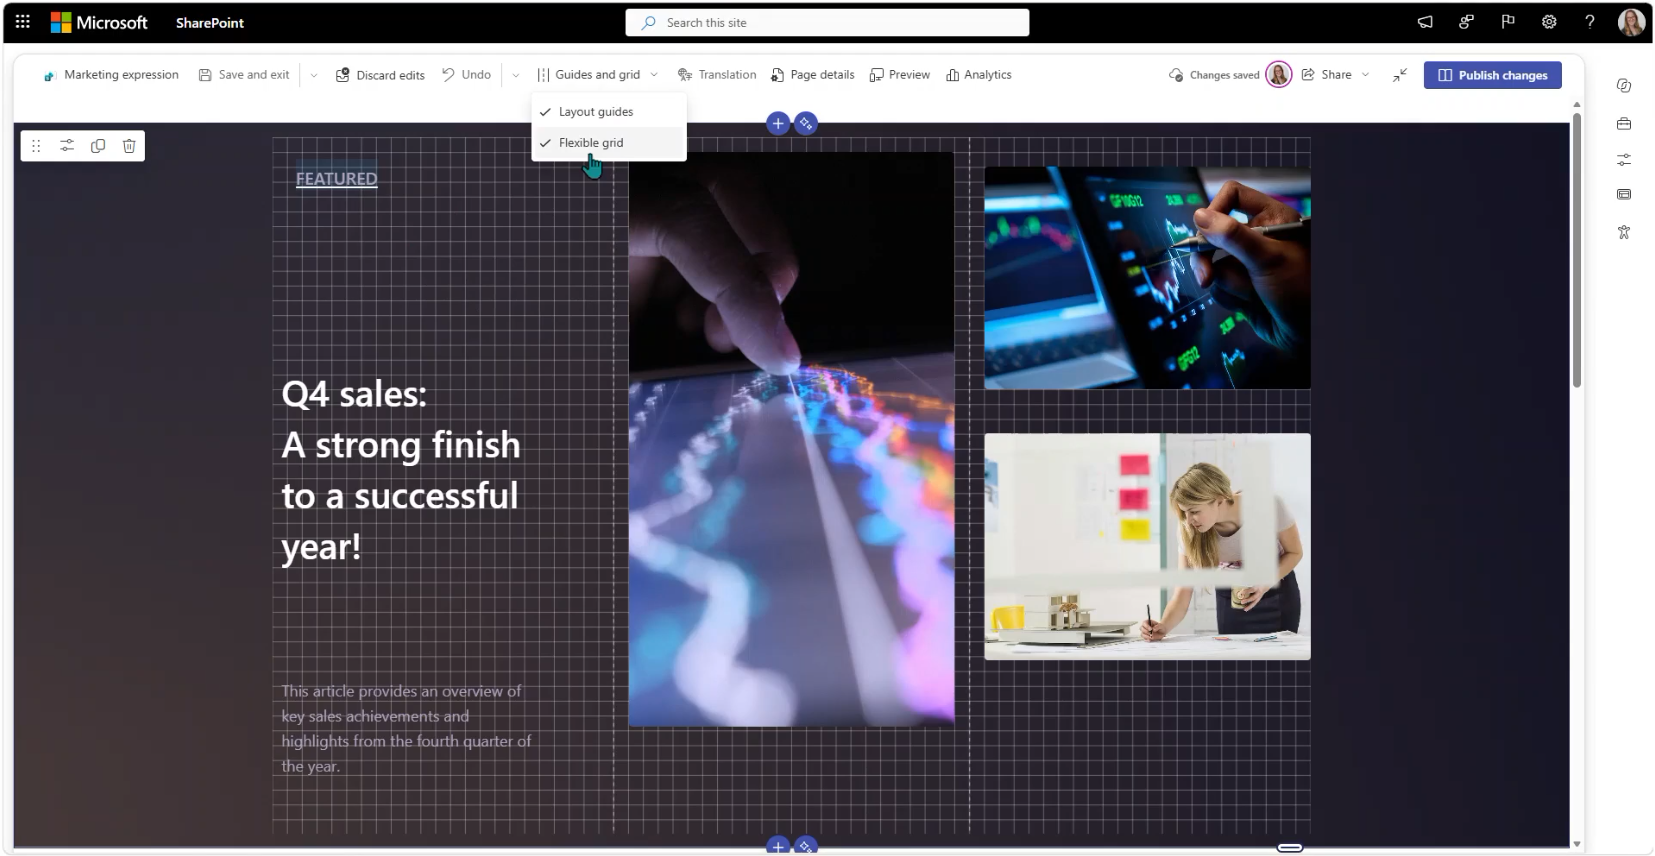
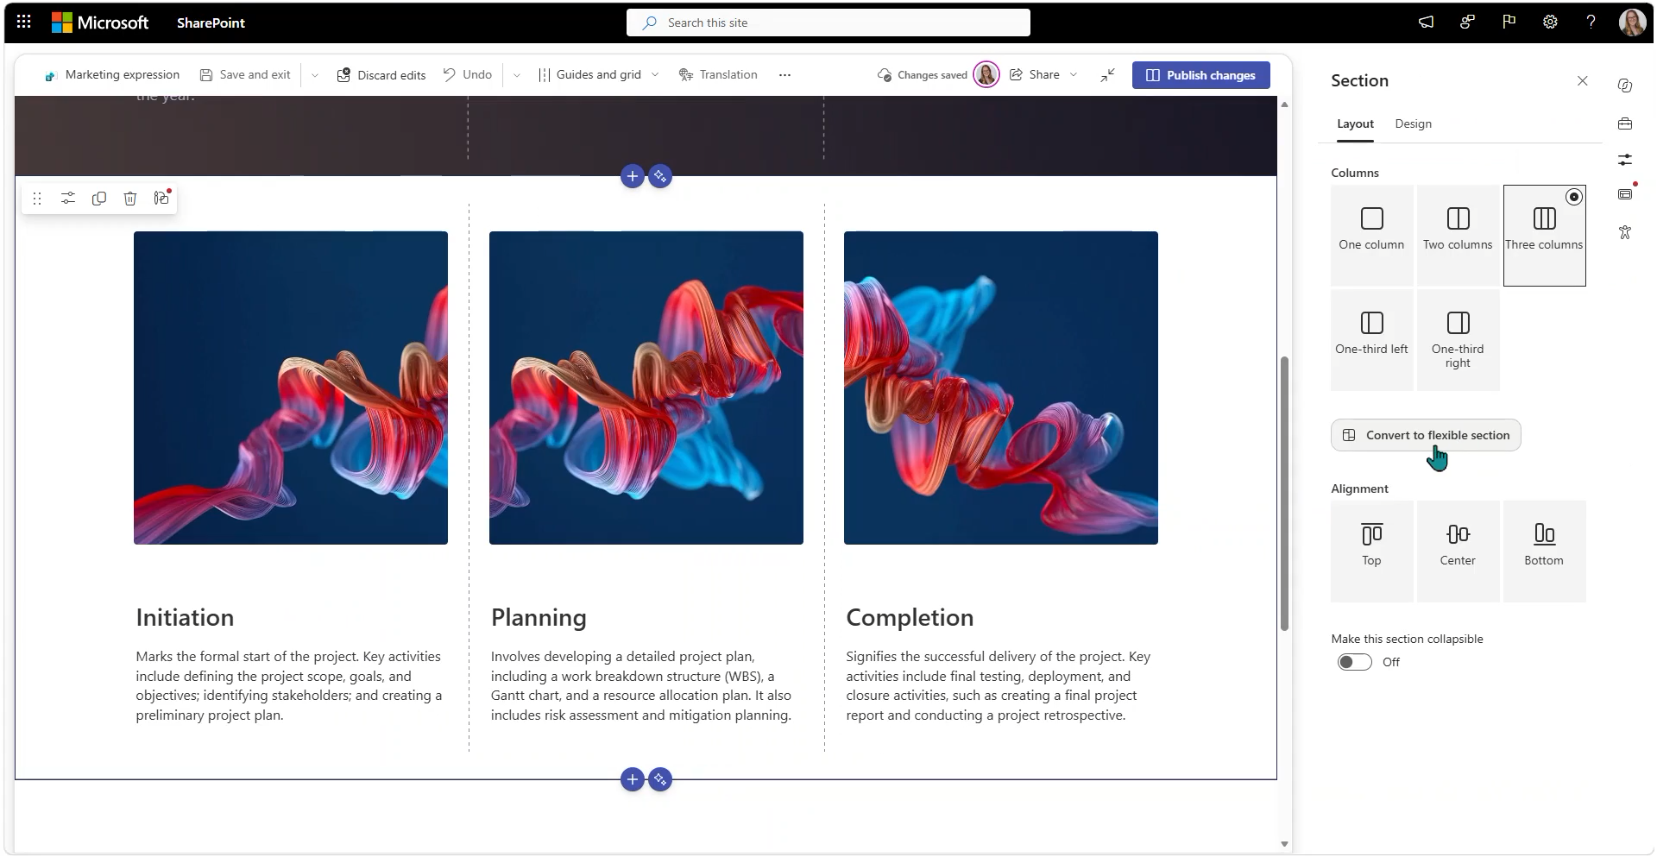
Microsoft has made some authoring improvements to flexible sections in SharePoint Online. These changes include better visual column layout guides, persistent grid layout guides, and the ability to convert existing standard sections into Flexible Sections while preserving existing content layouts. These changes were rolled out to General Availability during the month of August. No admin actions were required for the new features to become available in SharePoint Online.
The key change to the sharing experience is the new Hero Link. Like the current sharing links, the hero link will have embedded access and access-level designations. Unlike the current sharing link, hero links remain the same even after access requirements change, reducing the need to create and send new links.
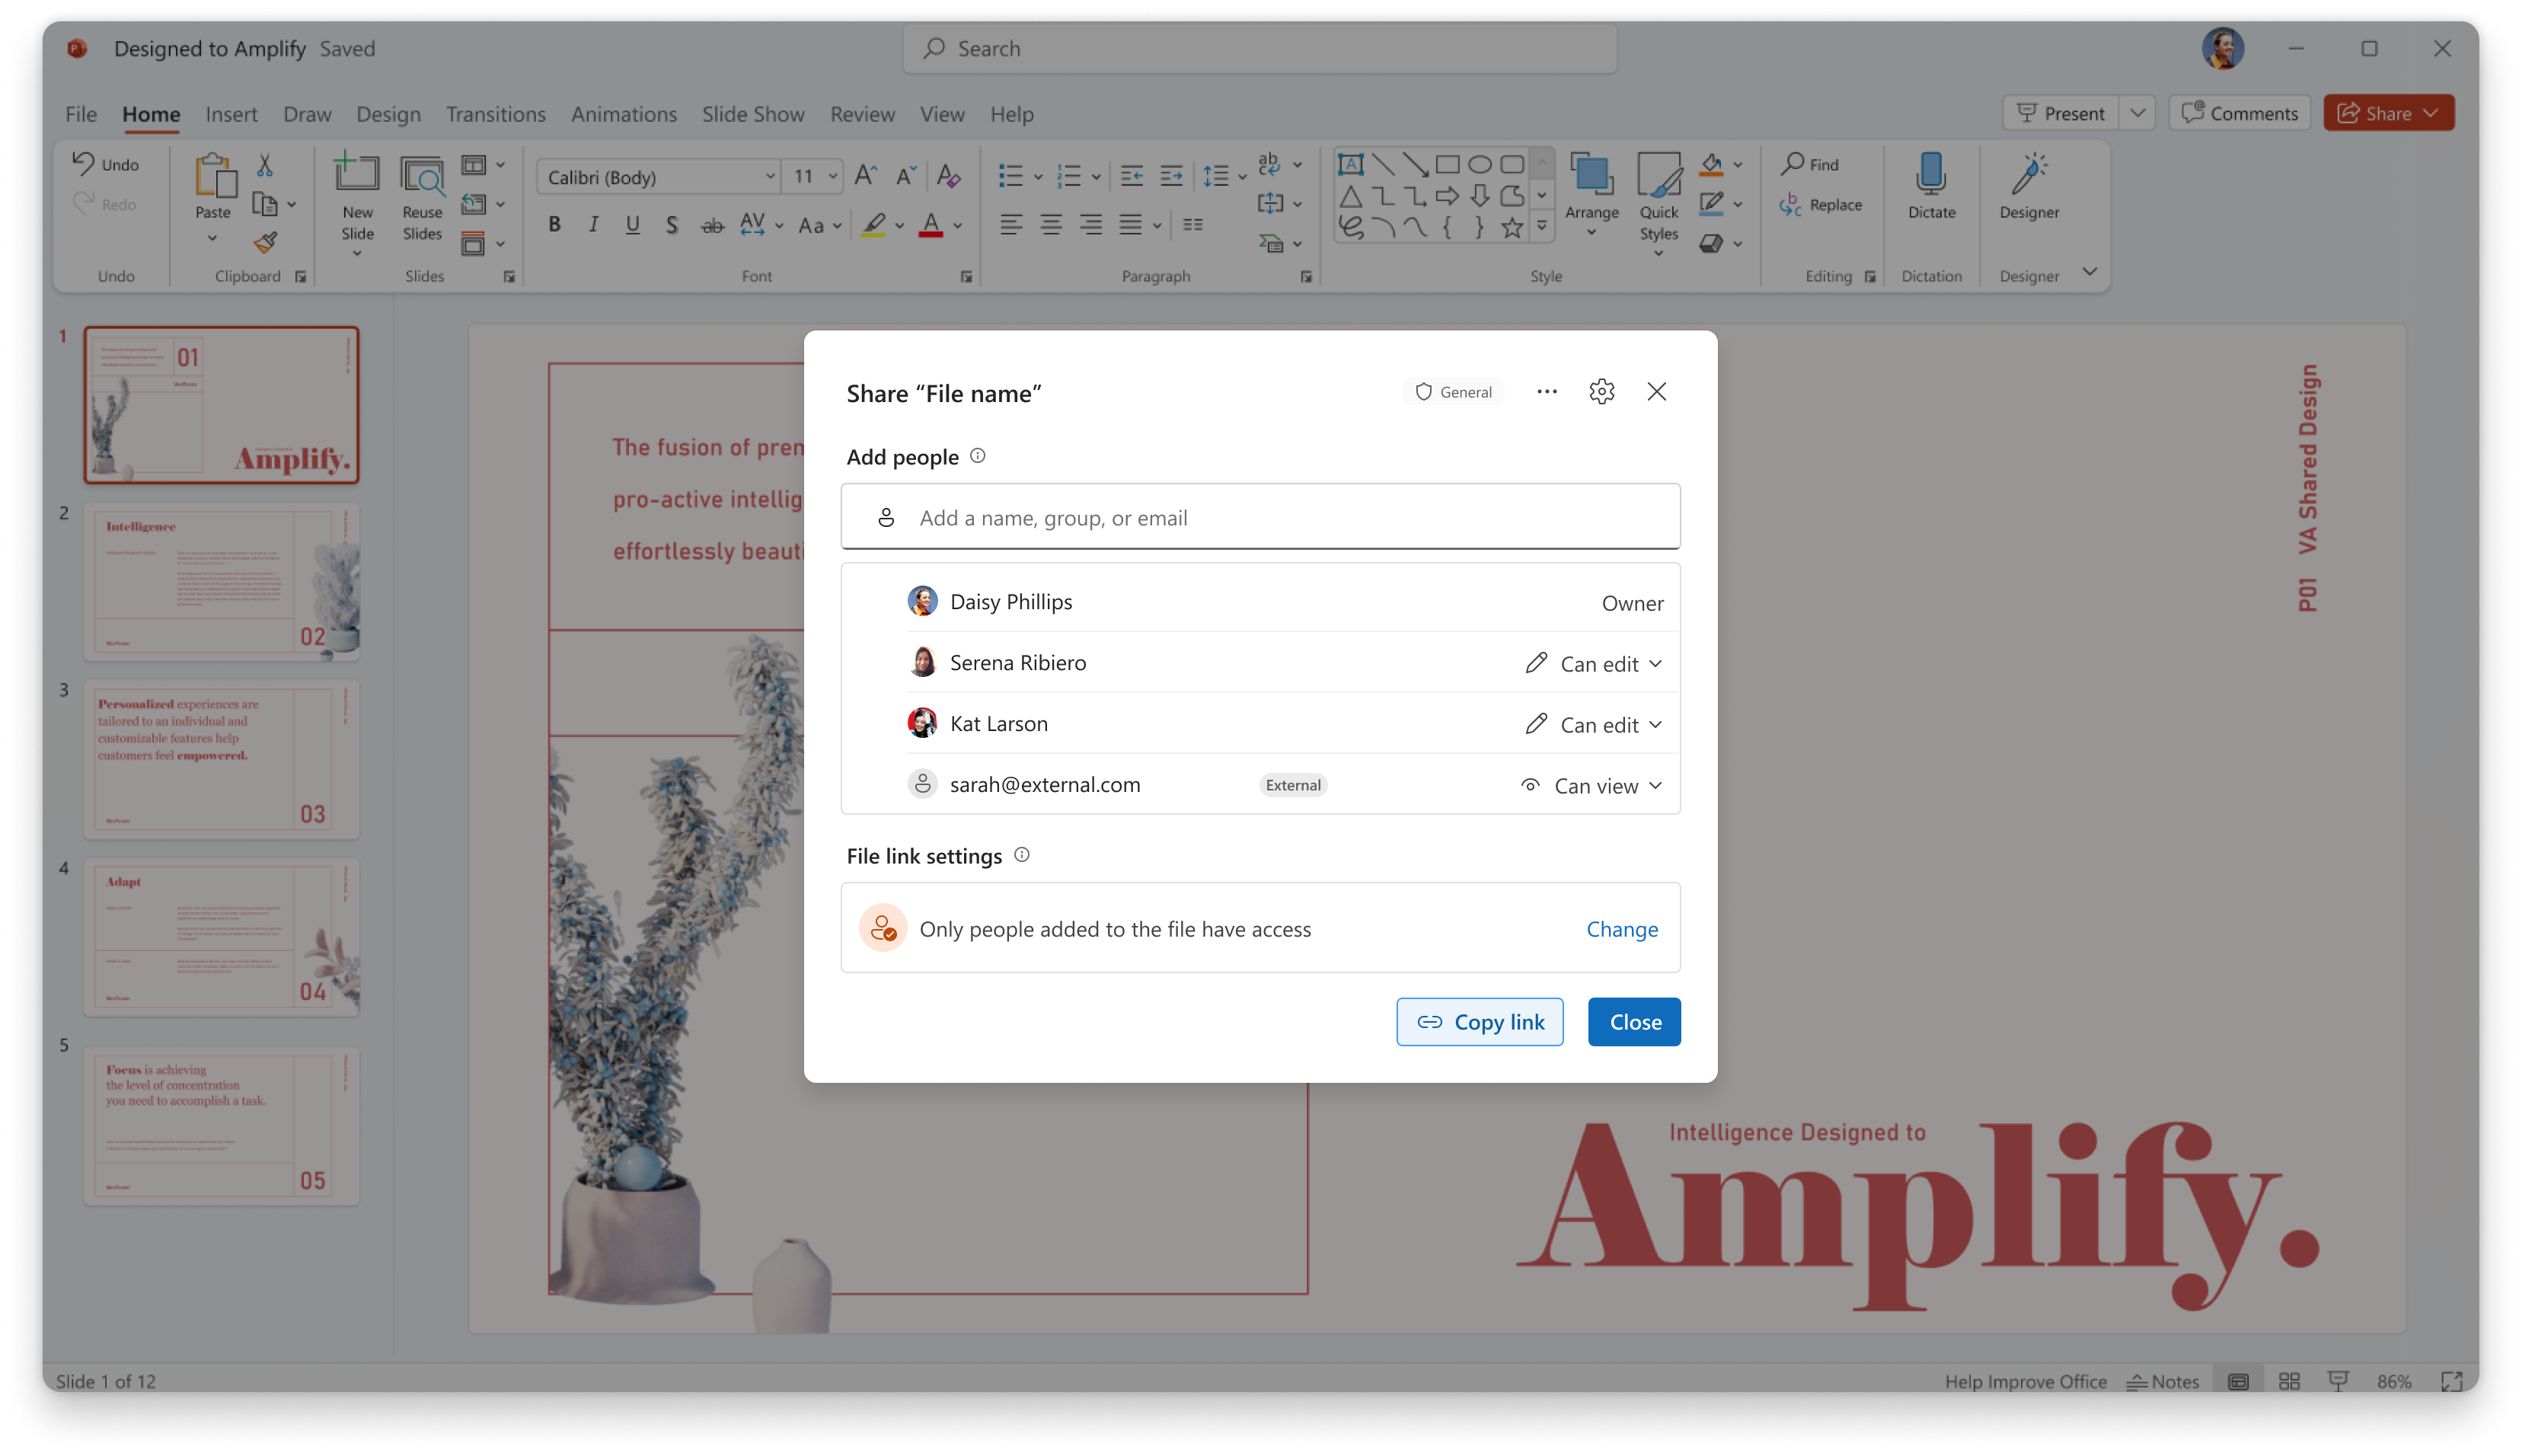 This change is expected to rollout out for all Availability (General, GCC, GCC High and DoD) mid-September 2026 through late October 2026.
According to What's New in Microsoft Entra: August 2026, Microsoft introduced several new identity and access management enhancements, including general availability of administrator control over Windows SSO prompts, Exchange Online attribute writeback to on-premises Active Directory through Cloud Sync, new Lifecycle Workflows capabilities such as what-if simulations, workflow cancellation, automated user attribute updates, and expanded dynamic email attributes, as well as support for external identity sign-ups without requiring email addresses. In public preview, Microsoft added device synchronization from on-premises Active Directory to Microsoft Entra Cloud Sync for Hybrid Join scenarios, automated detection and cleanup of sponsorless guest accounts, and backup/restore capabilities for Group Policy Objects in Microsoft Entra Domain Services. The overall theme of the release is improving automation, hybrid identity management, lifecycle governance, and secure access as organizations continue adopting AI-driven technologies.
Microsoft Intune has introduced Device Association for Windows Autopilot Device Preparation, a new Microsoft Intune capability that creates a trusted, hardware-backed connection between a Windows 11 device and an organization before enrollment begins. By using TPM-backed attestation and storing tenant affinity in UEFI firmware, organizations can ensure that a specific device receives the correct policies, applications, naming conventions, and out-of-box experience (OOBE) settings regardless of who signs in. The feature simplifies deployment by reducing user setup steps, automatically marking devices as corporate-owned, enabling device-targeted provisioning, and maintaining device trust through resets or OS reinstalls. IT administrators export device information, pre-associate devices in Intune, and then Windows automatically completes the association during OOBE. Microsoft positions this as a more secure, predictable, and device-centric onboarding model that can coexist with existing Windows Autopilot deployments while giving organizations greater control over device provisioning from the very start of the lifecycle.
Microsoft is rolling out a preview of a new app-building experience in Microsoft Copilot Cowork that allows users to create apps through natural-language conversations. The experience is designed to help makers move from an idea to a working app draft more quickly by using generative AI to create, refine, test, and publish applications. Microsoft also stated that a corresponding experience in Microsoft Copilot Studio is expected to arrive within the next few weeks.
From an administrative and governance perspective, this update is notable because apps created through these experiences remain aligned with existing organizational controls. Apps use Microsoft Entra authentication and are governed by current connector, data, security, compliance, environment, and sharing policies. Published apps will also be visible in the Apps > All apps experience within the Microsoft 365 admin center, giving administrators centralized visibility into what is being built and shared across the organization.
Another important change is the automatic routing of makers into isolated personal developer environments, based on organizational governance settings. These environments are protected by default configurations that administrators can adjust as needed. Microsoft also notes that organizations without environment routing already enabled will have routing automatically applied for apps created through these new experiences, although the change does not affect other resources created in Power Platform or Copilot Studio.
The Copilot Cowork preview is available through the Frontier Program for users who have a Microsoft 365 Copilot license and access to Cowork, with rollout beginning September 8, 2026 and expected to complete by September 14, 2026. Administrators should review Frontier Program onboarding requirements, validate app governance settings in the Microsoft 365 admin center, determine which users or security groups should have access during preview, and assess Copilot Credits and usage-based billing requirements before broader adoption.
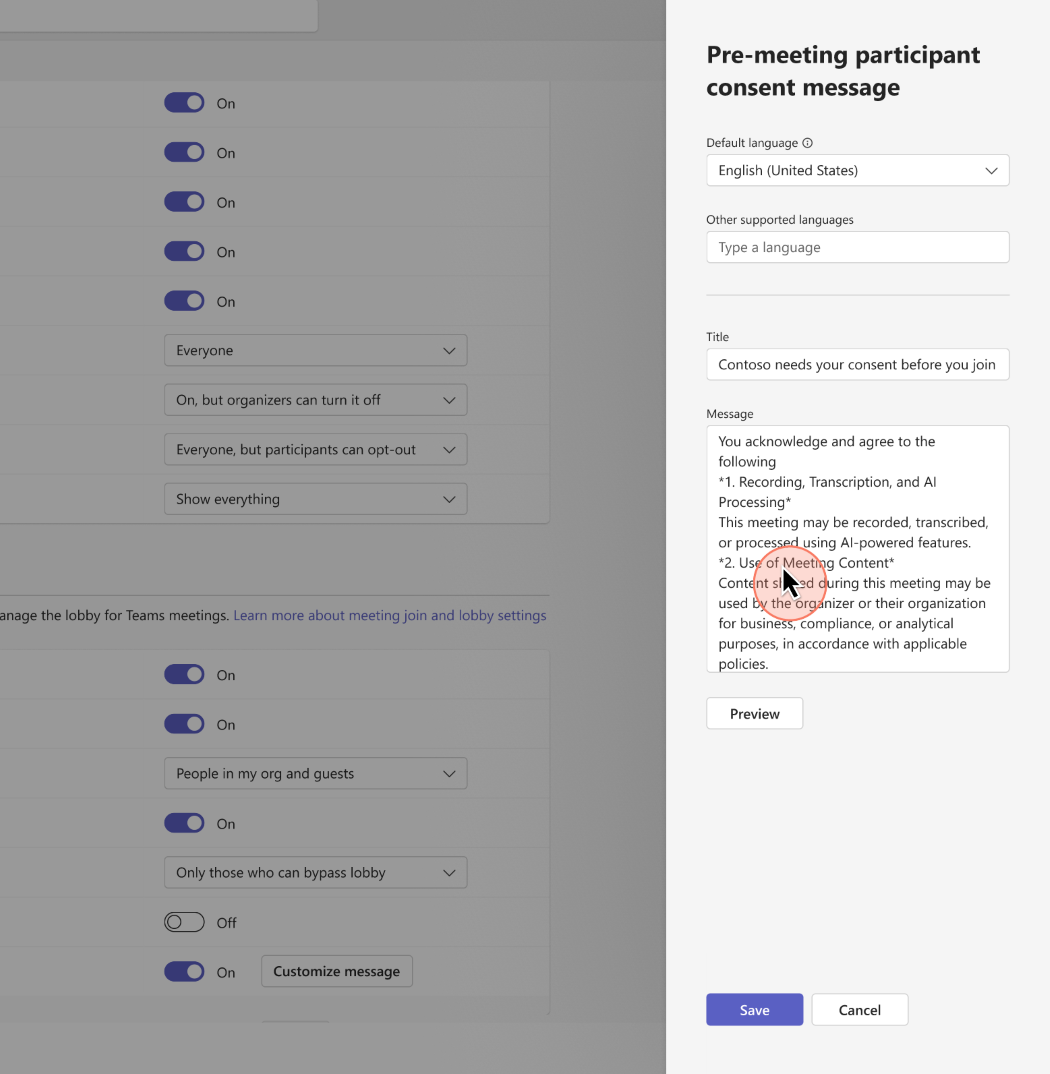
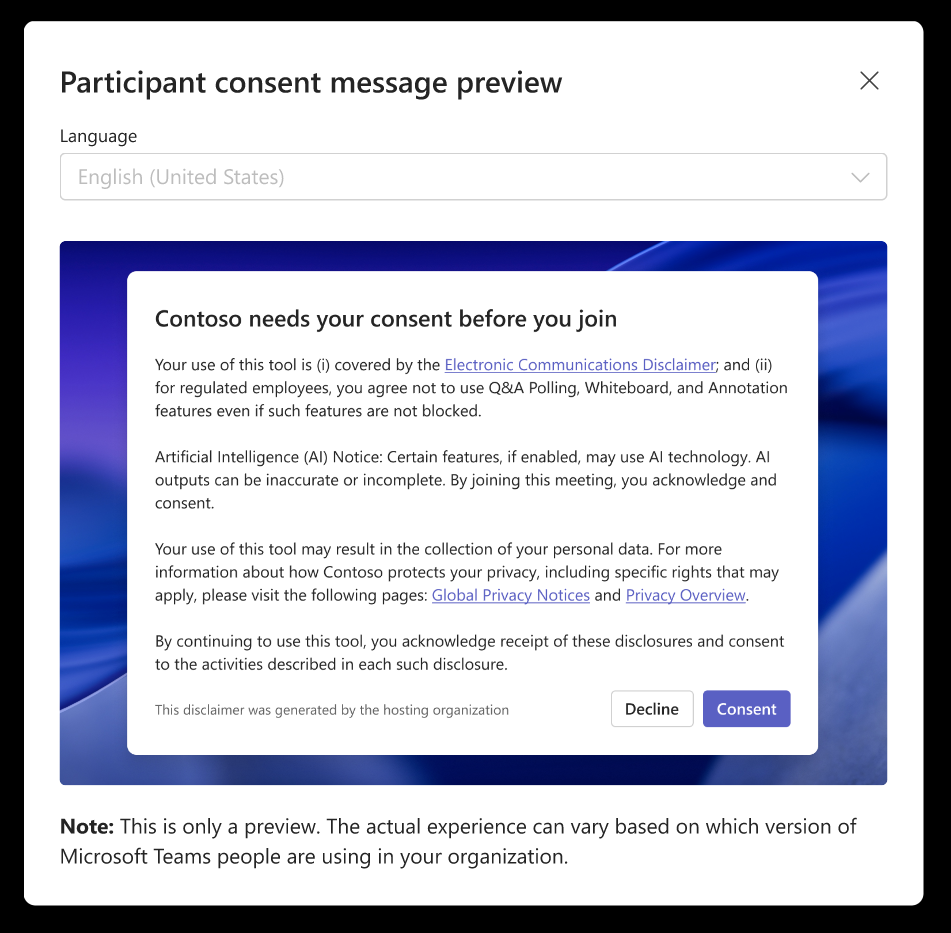
Microsoft Teams is introducing a new capability that allows admins to configure mandatory pre-meeting consent for participants. This feature helps organizations meet compliance and regulatory requirements by ensuring attendees acknowledge custom terms or disclaimers before joining meetings, such as recording notices or responsible AI usage guidelines. Consent acknowledgments are recorded in audit logs to support governance, investigations, and transparency.

Self-serve sync Copilot connectors enable users to securely connect their own external data sources, such as Jira Cloud and Confluence Cloud, to Microsoft 365 Copilot using their existing credentials and permissions. Content that users already have access to can be synchronized and made discoverable in Copilot Chat and Microsoft Search.
This capability helps users find relevant information across their work tools, reduce context switching, and gain greater value from Microsoft 365 Copilot while maintaining organizational governance through administrator controls.
Self-serve connectors are enabled by default. Before connectors become available to users, administrators can review and manage the available connectors in the Microsoft 365 admin center.
-
Users can securely connect supported external work sources using their own credentials and permissions.
-
Content from connected sources can become discoverable in Copilot Chat and Microsoft Search.
-
Administrators can enable or disable individual connectors.
-
Administrators can stage rollout to specific Microsoft Entra ID groups.
-
Administrators can control connector visibility and availability across the organization.